 ChatGPT
 Perplexity

This guide breaks down risk management in software development from the client's side: the four-phase process, the risk-plan artifact your partner should be producing, and the red flags that reveal a partner who isn't running one.
Highlights:
- Mature partners run a four-phase process: identify, score, plan, and monitor every sprint.
- No written risk plan or "we're agile" as an answer signals no real process.
- Vendor lock-in, key-person departure, and business continuity are risks partners rarely volunteer.
On October 20, 2025, a DNS resolution failure inside AWS's US-EAST-1 region cascaded into outages across dozens of dependent services. Companies that had never given a second thought to where their digital infrastructure sat suddenly found out the hard way. Some had a plan. Most didn't.
That gap, between teams who saw it coming and teams who didn't, is not luck. It's a process, and it's the same process behind every well-managed software development risk.
This isn't a process guide for dev shops. It's a buyer's guide — what mature risk management looks like from where you're sitting: the client, evaluating or already working with a technical partner, trying to figure out whether the people building your product are actually managing risk or just saying the word "agile" and hoping.
We'll walk through the same four-phase process and risk-plan artifact we run internally at Mind Studios, reframed as what you should expect to see your partner produce, plus the red flags that tell you they don't have one.
Want a second pair of eyes on your own project's risk exposure before it becomes a bigger investment than planned? Book a free consultation, and our team will walk through it with you.
Empower your project
with concrete tech
expertise
Contact Mind Studios

What real risk management actually buys you
Every software project carries risk. What separates a partner worth keeping from one worth replacing is whether that risk gets managed before it turns into your problem.
When your partner runs a real risk process, here's what changes about your outcomes:
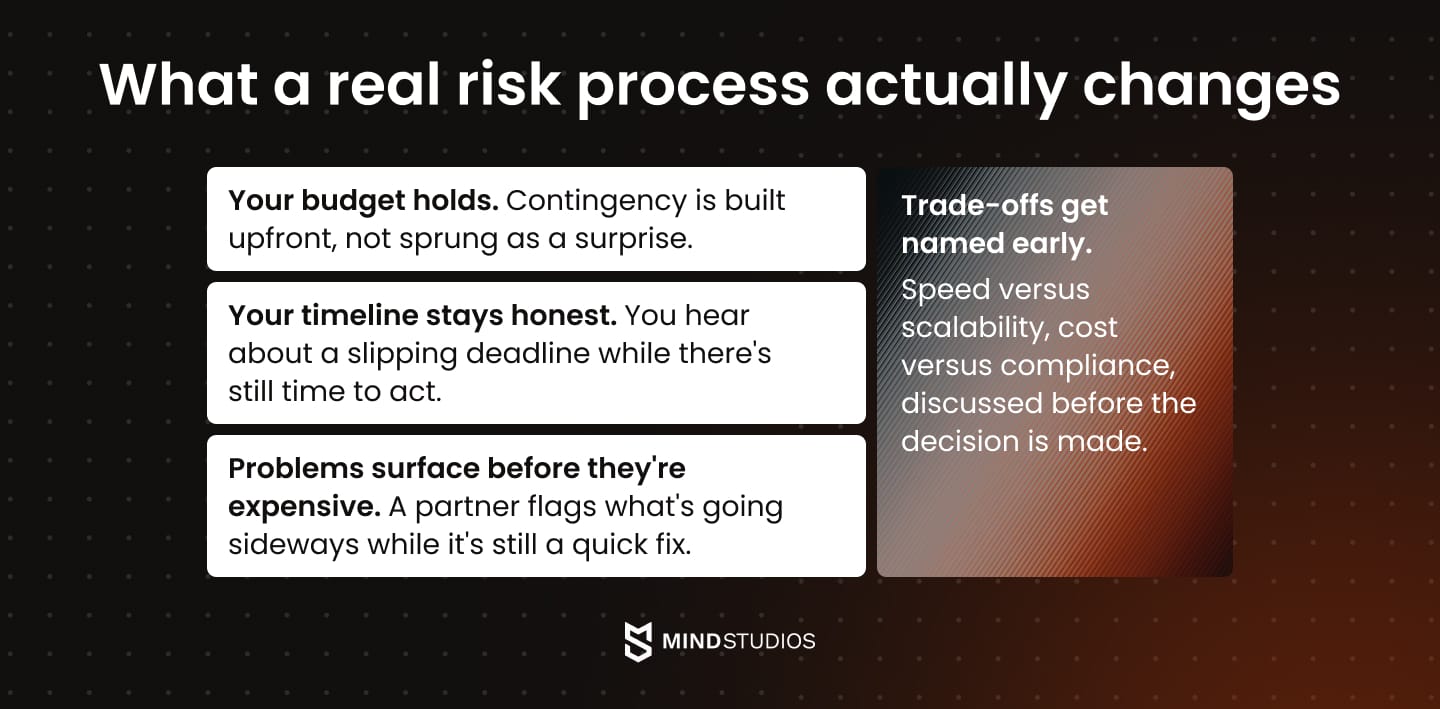
None of this is abstract upside. PMI's 2025 research on project performance found that organizations who build this kind of proactive discipline into how they run projects show markedly higher adherence to both budget and schedule than those who don't.
Risk management is one of the concrete practices behind that gap — it's ROI you can point to, not just a feeling of being better managed. Ignoring the risks of software development doesn't make them go away, but moves the cost to later, when it's more expensive to fix.
Every project of ours that's gone sideways, and I mean every one, traces back to the same thing: somebody saw the risk coming and didn't say it out loud, or nobody was looking closely enough to see it at all. The clients who stay with us for years aren't the ones who never hit a problem. They're the ones who found out we'd already flagged it three sprints earlier.
— Dmytro Dobrytskyi, CEO at Mind Studios.
Types of risks in software development
Not every risk looks the same, and a partner who only watches for one kind is watching for the wrong thing. Here's the compact taxonomy worth knowing before you look at anyone's risk plan.
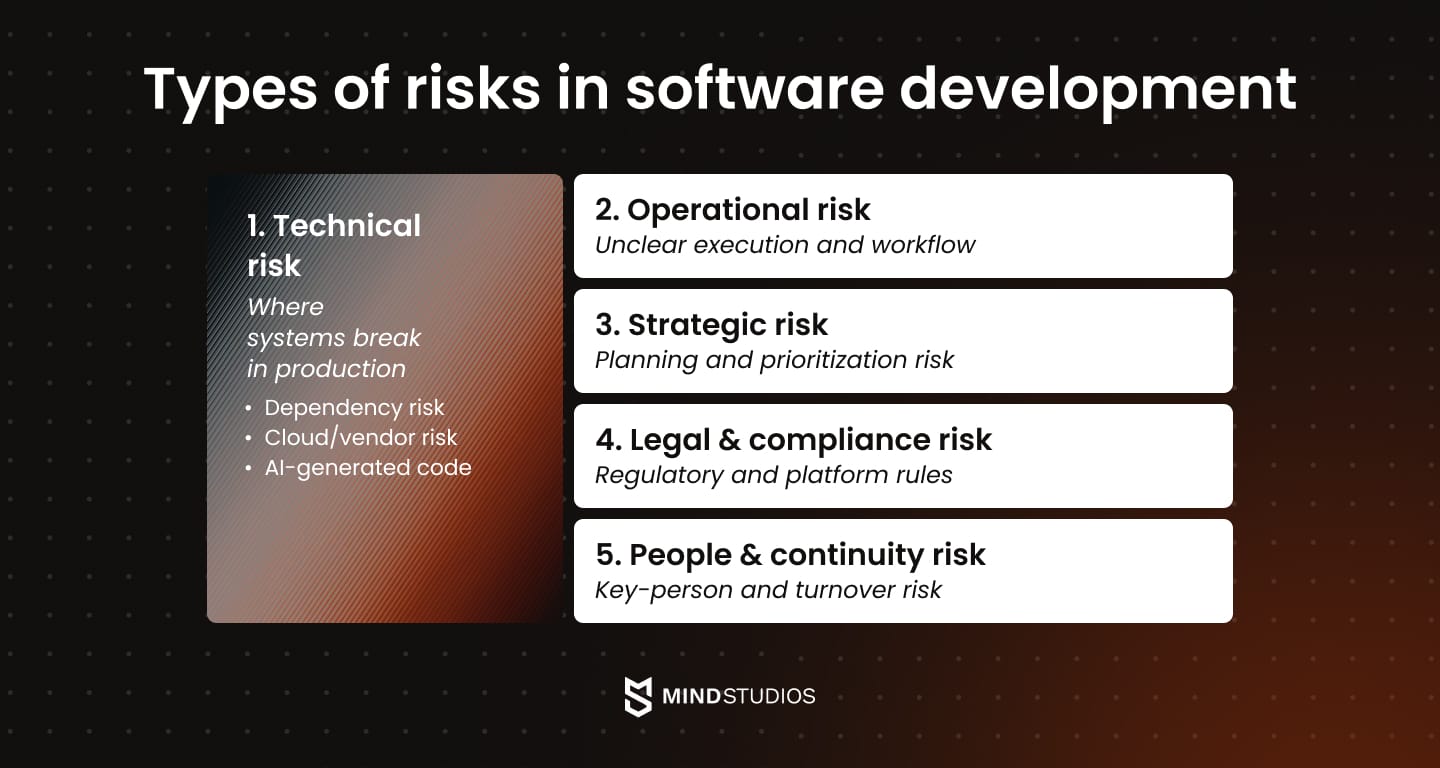
Technical risk
A dependency, integration, or architectural choice behaves differently in production than it did on paper. This category has expanded meaningfully in the last two years and now includes three sub-classes worth naming specifically:
- Third-party dependency and API deprecation risk. A payment processor or mapping API changes its terms or sunsets a version your product relies on, and you find out when something breaks.
- Cloud and vendor concentration risk. Your entire stack sits on one provider, one region, and when that provider has a bad day, so does your ability to stay scalable. We've handled exactly this exposure before: in the case of FITR, a client we've partnered with for 7+ years, the platform moved to AWS specifically to get out from under a single point of failure.
- AI-generated code risk. Unreviewed AI output that ships into production without a human checking whether it does what was intended. This is new enough that most teams don't have a policy for it yet, which is exactly the problem.
Mind Studios’ note: The pattern we see most often isn't AI writing bad code, it's AI writing code that passes review because it looks right, not because anyone verified it does what the ticket asked. We've started asking one extra question in QA specifically for AI-assisted PRs: not "Does this work?" but "Does this do the thing we meant?"
Operational risk
Execution-level issues: unclear dependencies between workstreams, slow decision-making, a QA process that doesn't catch what it should. A feature ships, breaks a workflow nobody tested, and support tickets spike before anyone traces it back to the release.
Strategic risk
Planning and prioritization choices that look reasonable in isolation but compound badly. A team builds the admin dashboard before the core user flow is validated, then has to rework both when user testing reveals the core flow was wrong.
Legal and compliance risk
Regulatory requirements specific to your industry or market, plus platform rules (App Store, Google Play, payment networks) that change without much warning. A healthcare product that didn't scope HIPAA-compliant data handling and security requirements from day one pays for it later, in rework and in delay.
People and continuity risk
What happens when the person who understands a system the best leaves, gets reassigned, or the relationship with your partner sours mid-project? This is where most of the damage that clients actually feel originates, and it's covered in more depth in The Risks of Changing a Team in the Middle of a Project.
None of these risk types operate alone. A cloud-concentration risk that materializes during a leadership transition is a worse day than either problem on its own, which is exactly why a real, secure risk process tracks all of them together, not one at a time.
Not sure which of these apply to your own project? Talk to our team, and we'll map your specific risk exposure together.
4 strategies for responding to risk
Once a risk is identified, your partner has to decide what to do about it. There are four options, and a mature partner picks deliberately between them rather than defaulting to the same one every time.
Risk avoidance
Some risks aren't worth taking on at all. If a client wants to add real-time video processing to a mobile app but the target devices can't handle the load without draining the battery in twenty minutes, the right call is to not build that feature as scoped, not to build it and hope.
| Pros | Cons | Use when |
|---|---|---|
| Fast to decide, no wasted engineering effort. | You give up whatever value that feature would have delivered. | The cost of failure outweighs any plausible upside. |
Risk mitigation
Some risks can't be avoided, only softened. A product launching during a known high-traffic event (Black Friday, tax season, an app store feature) can't skip the launch, but the team can add autoscaling, load-test ahead of time, and have a rollback plan ready so a spike degrades gracefully instead of taking the whole system down.
| Pros | Cons | Use when |
|---|---|---|
| You keep the value of the activity while working to reduce the damage if things go wrong. | You still absorb some consequences; mitigation isn't elimination. | The activity has to happen, but the downside can be softened in advance. |
Risk transfer
Some risks are better handled by someone who already has the expertise. Bringing in a specialist partner for a payment-processing integration, carrying cyber-insurance for a data breach, or using a managed database service instead of running your own are all forms of transfer — vetted third-party solutions absorbing part of the risk for you.
| Pros | Cons | Use when |
|---|---|---|
| Often faster than building the expertise in-house, and it frees your core team to focus on what differentiates your product. | It costs money, and you give up some direct control over that piece. | The risk sits outside your team's core expertise, and getting it wrong is expensive. |
Risk acceptance
Sometimes the right call is to accept a risk on purpose, with eyes open, and document why. A company might knowingly delay a nice-to-have accessibility improvement to hit a fundraising-critical launch date, accepting that risk because the trade-off is worth it, and planning to fix it in the next sprint. That's acceptance done right — a deliberate decision, documented.
| Pros | Cons | Use when |
|---|---|---|
| Costs nothing upfront. | You carry the full consequence if the risk materializes. | The potential impact is genuinely low, or the upside of moving forward clearly outweighs it, and the decision is made consciously rather than by default. |
No real project runs on one strategy alone. Most risk plans mix all four, choosing per risk rather than per project. That mix, and the reasoning behind it, is exactly what should show up in the plan your partner shares with you.
What a real risk process actually produces
This is the process itself — the same one we run at Mind Studios on every engagement. Skipping any of these four phases is exactly where things go wrong.
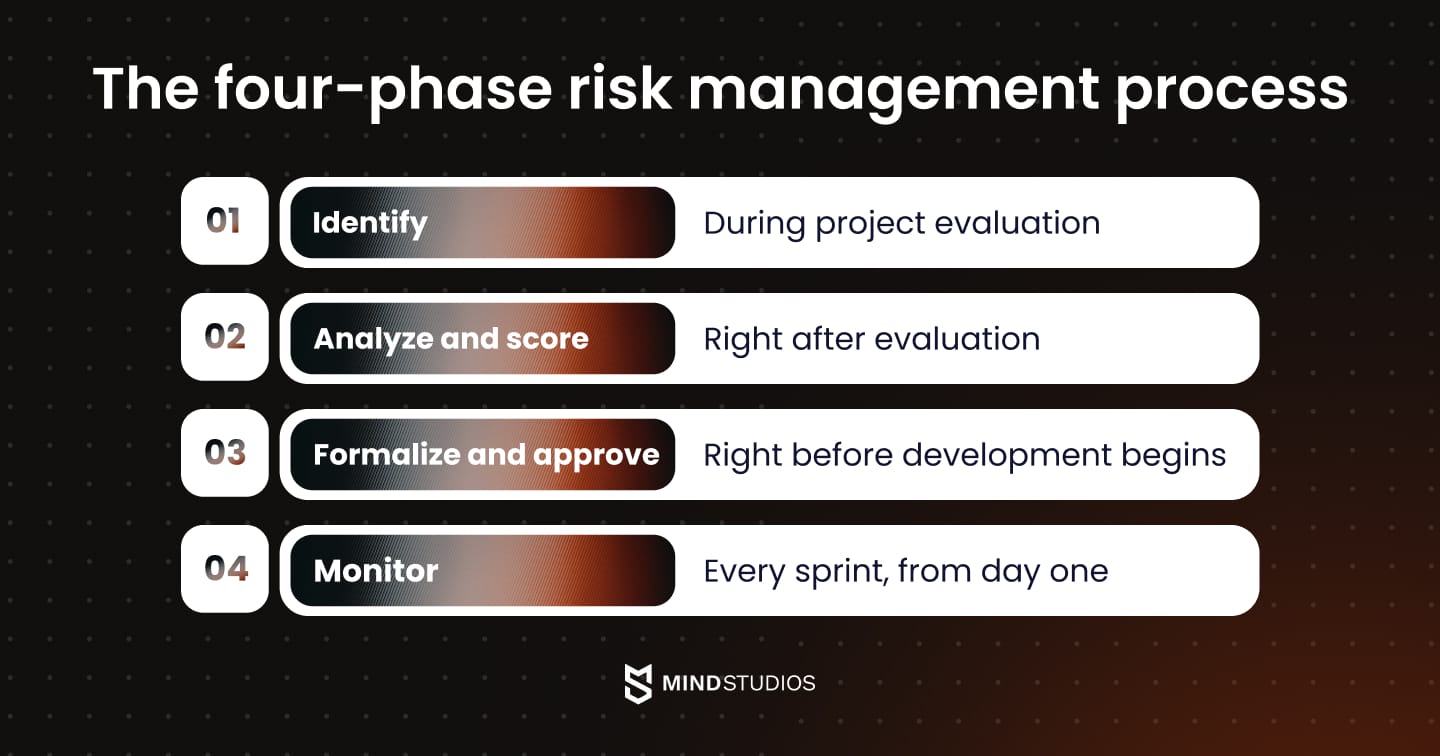
Phase 1: Identify, during project evaluation
Before development starts, the project manager pulls developers and designers into a session built around one question: what could go wrong here, specifically, and what would trigger it?
The team works from three angles: what's gone wrong on similar projects before, where this particular project is exposed, and what the impact would be if each risk actually happened.
What this means for you: the risks on your project get named before a single sprint starts, not discovered mid-build.
Phase 2: Analyze and score, right after evaluation
Every identified risk gets categorized and scored, factoring in project complexity, testing depth, and dependencies between teams. This phase produces a defined set of consequences for each risk: potential losses to you, business impact, reputational exposure, and legal exposure.
What this means for you: you're not told a risk exists in the abstract. You're told what it costs if it materializes.
Phase 3: Formalize the plan and approve it with you, right before development begins
This is where the risk plan gets built, and it's a specific artifact, not a paragraph in a proposal. Each row covers:
| Field | What it captures |
|---|---|
| Risk definition | The problem, stated in one clear line — e.g. "lack of server capacity," "Play Store release delay." |
| Trigger | What tells the team the risk has materialized. |
| Probability score and impact score | Scored independently from each other. |
| Value | Probability × impact — sets priority. |
| Main strategy and alternate strategy | Which of the four responses applies, plus a backup if the primary one isn't viable. |
| Action plan | A numbered, owner-named sequence for what happens if the risk hits. |
Here's what that looks like side by side:
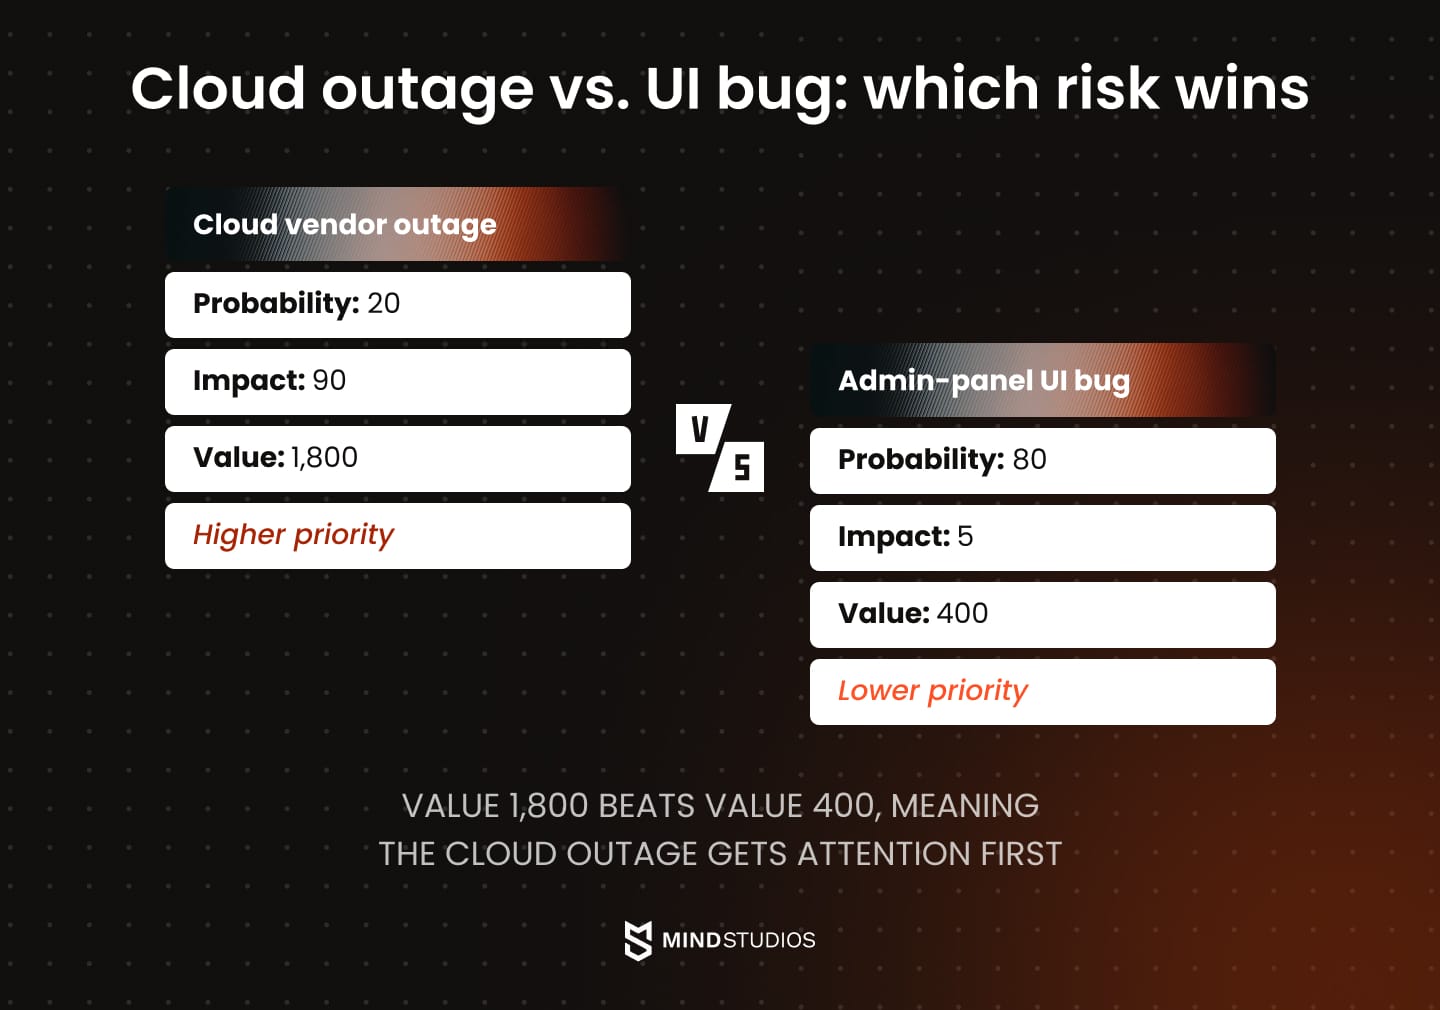
Scoring isn't always clean. Impact and probability get debated, sometimes disagreed on between the PM and the client, and that's the point where the plan earns its keep: the conversation happens before development starts, on paper, instead of surfacing as a dispute mid-build.
What this means for you: this plan is approved with you, not delivered to you after the fact. You see costs, owners, and trade-offs before development starts, not after something goes wrong.
Phase 4: Monitor, from day one, checked after every sprint
A solved risk can resurface. Triggers get pulled from user feedback and QA reports too, not just the original plan, and monitoring gets built into every sprint going forward rather than treated as a one-time setup task.
What this means for you: the plan doesn't go stale. It's a living document your partner is actually checking, sprint over sprint.
Who runs this day-to-day is typically your project manager — that role is covered in more depth in The Role of Project Managers. And the shape this process takes can vary somewhat depending on your partner's chosen SDLC model, though the four phases above hold regardless of methodology.
Risk identification also leans heavily on how well your project's requirements were scoped up front; a thin requirements document tends to produce a thin risk plan, because you can't name what you haven't defined.
Curious what a risk plan like this would look like for your own project? Contact our team, and we'll show you the plan before you sign anything.
The red flags that tell you your partner has no real process
The red flags below are what's missing when that process isn't real.
We hear versions of most of these when a prospective client describes what went wrong with a previous partner. The "it's all in the PM's head" one comes up more than any other.
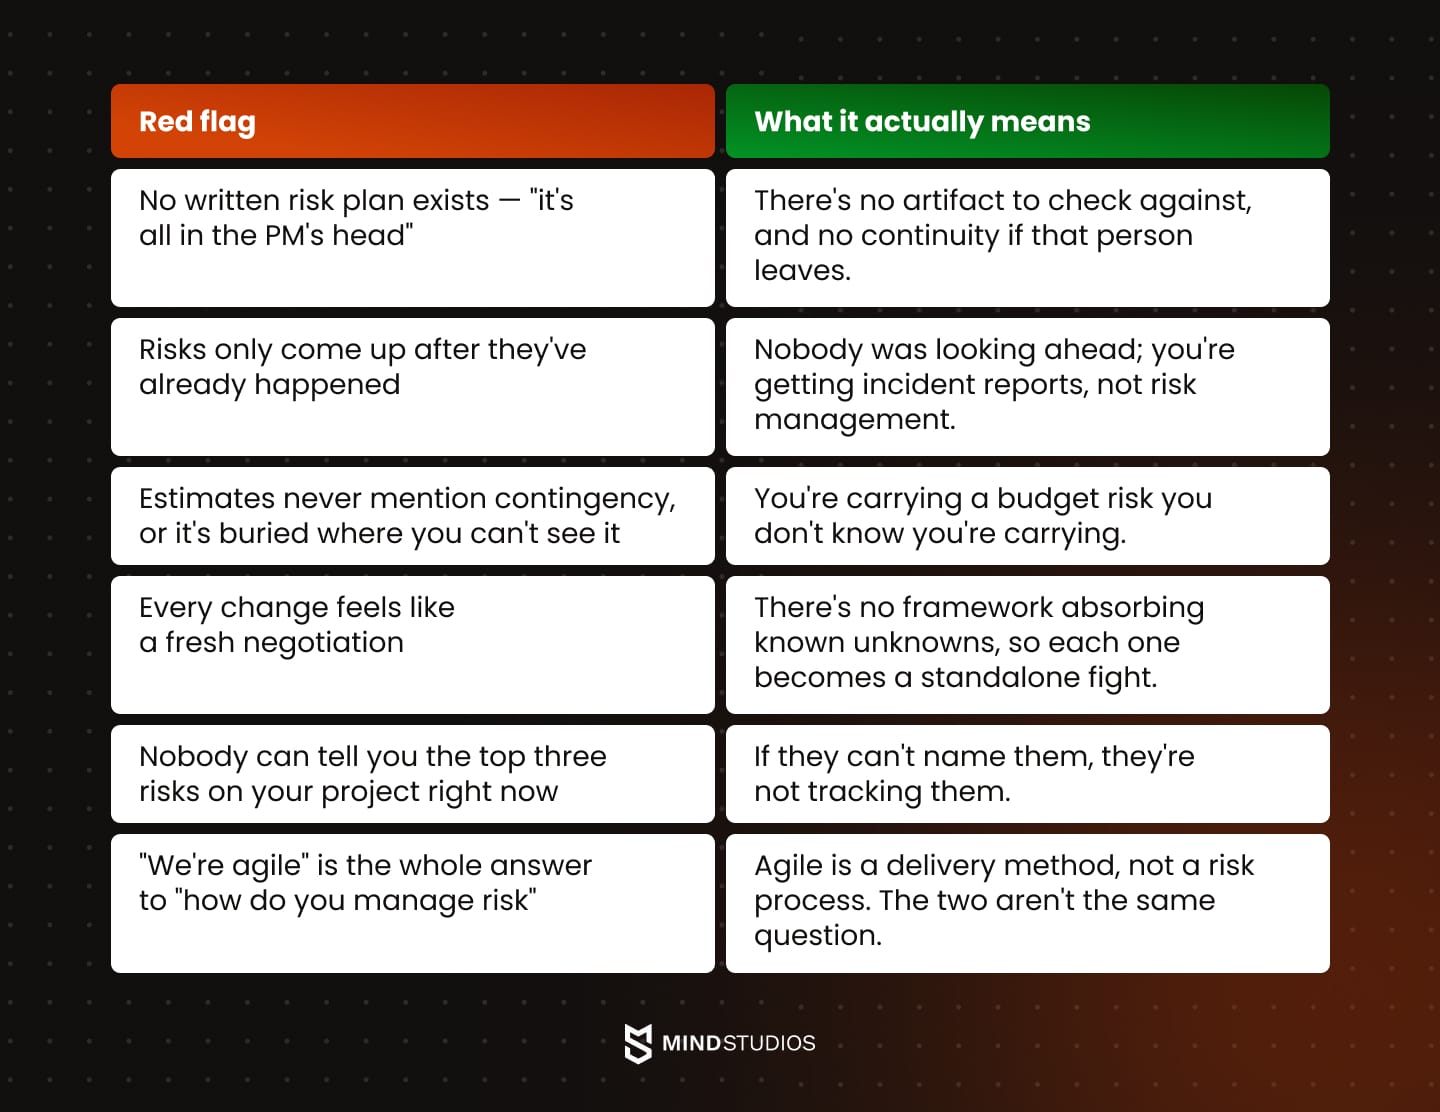
There's a second category worth naming separately, because these are risks vendors have less incentive to bring up on their own:
- Code and knowledge lock-in. If your product only makes sense to the people who built it, and there's no documentation a new team could pick up, you don't own your own codebase in any practical sense. Require documentation as a contractual deliverable, not an afterthought.
- Key-person departure with no handover plan. If one engineer or PM leaving would stall your project, that's a risk your partner should have surfaced, not one you discover the week they resign. Ask what the bench looks like, and how a handover would actually work.
- Vendor business continuity. Partners close, get acquired, or restructure. Ask what happens to your project, your code, and your data if your partner isn't around in six months, and whether that answer is in writing anywhere. This is also where your choice of engagement model matters: some structures make a transition easier than others.
What to ask, and what a real answer sounds like
Red flags tell you what to notice. These are the questions that surface them directly.
| Ask this | A strong answer | A weak answer |
|---|---|---|
| "Can I see the risk plan for my project?" | A specific document, with your project's actual risks named, scored, and owned. | "It's more of an internal thing," or a generic process slide deck. |
| "What are the top three risks on this project right now?" | Three specific answers, on the spot. | A pause, then something vague like "scope creep, I guess." |
| "How is contingency built into this estimate?" | A clear percentage or line item they can point to. | "We build in some buffer" with no number attached. |
| "Who is the backup if my lead engineer or PM leaves?" | A named person or a described bench, plus a handover process. | "That hasn't come up" or no real answer. |
| "What happens to my code and data if this partnership ends?" | Documented terms, in writing, that predate the question. | Reassurance with nothing in the contract to back it up. |
The risks worth paying attention to are usually the ones the client didn't think to ask about. Any partner can answer the questions you bring to the table. What tells you something is what they bring to it unprompted. And when you ask to see the risk plan, watch the reaction as closely as the document. A partner with a real process hands it over without blinking. A partner without one gets defensive, or starts improvising one on the spot.
— Anton Baryshevskiy, CBDO at Mind Studios.
The fastest way to find out where your partner stands: ask to see the risk plan. Not a process description. The actual document, with actual risks named for your actual project. A partner who has one will hand it over without hesitation. That reaction alone tells you most of what you need to know.
Now you can tell the difference
Software development risk management was never about paperwork. It's the visible difference between a partner who thinks ahead and a vendor who reacts.
A vendor without a real risk process isn't necessarily dishonest. They may genuinely believe "we're agile" is a complete answer, right up until something goes wrong and they're improvising a response in real time.
You now know what that process looks like: four phases, a real artifact with named owners and scored risks, and monitoring that doesn't stop after kickoff. That's exactly what separates a vendor from a long-term partner. You also know the tells when it's missing. Not to make you distrust every partner, but to give you a way to check.
If you want to see what a risk plan for your own project would actually look like, book a free consultation. We'll map your project's specific exposure and hand you the actual plan before you sign anything.